Cybersecurity
-

Abstract: Faster evolving technologies, new peer adversaries, and the increased role of non-government entities changes how we think about decisions to develop and adopt new technology. Uncertainties about technology “shelf life,” adversary intentions, and dual uses of technology complicate these decisions. This seminar will discuss the use of mathematical models and optimization methods to provide insight on technology policy issues. These issues include: balancing risk and affordability during technology research and development; timing technology adoption; and understanding adversary responses to new technologies. Examples will be discussed from offensive cyber operations and synthetic biology. We will conclude by discussing implications for how policy analysts and policy makers think about technology and security.


About the Speaker: Philip Keller is a National Defense Science and Engineering Graduate Fellow at Stanford. He is completing his PhD in Management Science & Engineering. He studies technology policy problems posed by new technologies. His research is highly interdisciplinary, drawing on methods from engineering risk and decision analysis, game theory, and operations research. His professional experience includes conducting studies and analysis for the Department of Defense and the Department of Homeland Security at RAND and the Homeland Security Studies and Analysis Institute. Previous study topics include unmanned aircraft operations; nuclear terrorism; offensive cyber operations; and military force structure. Philip holds a BS in Mathematics and an MS in Defense and Strategic Studies.

Predoctoral Fellow CISAC
Seminars
Paragraphs

Technical and operational realities make it prohibitively difficult to adapt a Cold War paradigm of “deterrence stability” to the new domain of cyber warfare. Information quality problems are likely to forestall the development of a cyber equivalent of the strategic exchange models that assessed deterrence stability during the Cold War. Since cyberspace is not firmly connected to geographic space the way other domains are, it makes modeling extremely difficult as well as muddles neat conceptual distinctions between “counterforce” (military) and “countervalue” (civilian) targets. These obstacles seriously complicate U.S. planning for a credible cyber “assured response,” and also present substantial challenges to potential adversaries contemplating cyber attacks against U.S. interests. To create a maximally effective deterrent against cyber threats, the United States should seek to maximize the challenges for possible opponents by creating a cyber “strategy of technology” emphasizing resilience, denial, and offensive capabilities.

All Publications button
1
Publication Type
Journal Articles
Publication Date
Journal Publisher
Strategic Studies Quarterly
Authors
Number
4
-

Abstract: Cybersecurity depends heavily on civilian cyber defense, which is decentralized, private, and voluntary. Although the structure of this field stands to have a profound impact on national and international security, its history is rarely subject to critical or comparative analysis. Why is civilian cyber defense organized this way? There are at least three plausible explanations for the origins and evolution of cyber defense as an organizational field: technology, bureaucracy, and ideology. I examine the influence of each factor during the formative years of the Internet in the United States. From the beginning, malware was described in terms of infectious disease (viruses and worms), so I use public health to provide comparative context for cyber defense. I find that technological determinism explains far less about the genesis of this field than often assumed. Bureaucratic politics are also insufficient. Therefore, I argue that the American ideology of anti-statism is necessary to explain civilian cyber defense, and this family of ideas has important implications for security cooperation at home and abroad.

About the Speaker: Frank Smith is a Senior Lecturer with the Centre for International Security Studies and the Department of Government and International Relations at the University of Sydney. His teaching and research examine the relationship between technology and international security. His book, American Biodefense, explains why the U.S. military struggled to defend itself and the country against biological warfare and bioterrorism. His current research examines cyber security cooperation; he is also analyzing the potential impact of quantum computing on international relations. Previously, Smith was a visiting scholar with the Institute for Security and Conflict Studies at the Elliott School of International Affairs, a research fellow with the Griffith Asia Institute, and a pre-doctoral fellow with the Center for International Security and Cooperation at Stanford University. He has a Ph.D. in political science and a B.S. in biological chemistry, both from the University of Chicago. 

Frank Smith Senior Lecturer Speaker Centre for International Security Studies; Department of Government and International Relations, University of Sydney
Seminars
Authors
News Type
News
Date
Paragraphs

Following tragic terrorist attacks committed by ISIS agents in Paris last week, the online hacker group Anonymous declared in a video that it would launch a cyber-attack on ISIS.

The masked Anonymous speaker in the video warns ISIS, in French, to be prepared for a massive retaliation.

The "hacktivist" group has been tangling with ISIS since it attacked the Charlie Hebdo magazine's office in Paris last January, taking over email and social media accounts, or crashing public Islamic State websites by overwhelming them with traffic.

Anonymous members are already boasting that they have taken down ISIS-related websites and several thousand messaging or social media accounts.

Herbert Lin, senior research scholar for cyber policy and security at Stanford's Center for International Security and Cooperation and a research fellow at the Hoover Institution, says that Anonymous' activities against ISIS provide a useful nuisance to the terror group, but aren't quite legal under U.S. laws.

What types of attacks will Anonymous likely launch?

They don't have the capability to do the kind of things that a nation-state could do. The NSA, for instance, has the ability to place implants into hardware. Anonymous is more likely to engage in hacking that is less sophisticated. For example, ISIS almost certainly doesn't have a bank account that is coupled to the international banking system; they operate outside that particular channel. But they have lots of money, some of which may be stored in a personal- or business-like bank account. If so, that means that it can be hacked the same way that your bank account can be hacked, by cracking the username and password.

Similarly, Anonymous has been successful in the past at getting into ISIS members' email and messaging accounts, or taking down their Twitter feeds, which can disrupt their ability to coordinate terrorism-related activities; we can expect more in the future.

What kind of damage can Anonymous do to ISIS, and how effective will it be?

This approach clearly isn't the silver bullet that takes down ISIS, but attacking messaging abilities or bank accounts are useful harassing activities. Repairing these systems and accounts wastes ISIS's time and annoys them – the same way it does to you when your personal accounts are hacked. Having to untangle these messes can disrupt their overall operations, which is a perfectly good thing to do.

Do governments frown upon private citizens taking this type of action?

I think that the official line of the U.S. government on this is that it violates U.S. law for Anonymous to take on ISIS. It's vigilante justice in cyberspace, which is illegal under the Computer Fraud and Abuse Act. On the other hand, while the U.S. government might not be favorably disposed to it, I think it is unlikely that any prosecutor would actually indict an American for harassing ISIS in this way. And maybe the Anonymous hacker will uncover some information that is really useful to the U.S. government and be inclined to pass it along.


Hero Image
anonymous screnshot
A screenshot from the hacker collective Anonymous' online declaration that it would increase cyber attacks on ISIS in the wake of the Paris terror attacks.
All News button
1
-

- This event is offered as a joint sponsorship with the Hoover Institution - 


Abstract: Writing on matters relating to the cyber era dominate government and academia alike.  Much of the focus tends to be on either the technical aspects or questions about cyber threats and warfare. Much less attention has been on the advent of the cyber era for the intelligence community. While there can be no doubt that the technological age in which we find ourselves today is new, there is a related question about the extent to which it has changed the work of the intelligence community. This talk argues that to find an answer, it is imperative to consider previous technological revolutions and consider how the intelligence community adapted. Only by doing so is it possible to address the issue of whether intelligence is the cyber era is a revolution or evolution.

About the Speaker: Professor Michael S. Goodman is a Professor in ‘Intelligence and International Affairs’ in the Department of War Studies, King's College London.  He has published widely in the field of intelligence history, including most recently The Official History of the Joint Intelligence Committee, Volume I: From the Approach of the Second World War to the Suez Crisis (Routledge, 2014), which was chosen as one of The Spectator’s books of the year.  He is series editor for ‘Intelligence and Security’ for Hurst/Columbia University Press and is a member of the editorial boards for five journals, including the three main intelligence ones. He is currently on secondment to the Cabinet Office where he is the Official Historian of the Joint Intelligence Committee.

Michael Goodman Professor in Intelligence and International Affairs Speaker King's College London
Seminars
Authors
News Type
News
Date
Paragraphs

U.S. Senator John McCain told a select group of Stanford undergraduate students that technological innovation had created both unparalleled opportunities for the United States as well as new national security risks, during a visit to Silicon Valley this week.

“This has changed the world,” Senator McCain told the students as he held up his smart phone.

“This is the biggest change in our ability to inform and educate than any invention since the printing press.”

However, McCain told students that he believed the United States needed to develop a clearer policy for responding to cyber attacks from foreign nations.

Image
img 3458
“You’ve got to accept a fundamental premise, that cyber attacks are an act of war…but that doesn’t mean you’re going to war in a conventional fashion,” he said.

“The people who are doing these cyber attacks have to realize that the costs will be higher than the benefits of the attack. Everybody has to know that there will be a price to pay for it.”

McCain called on the students, who included several computer science majors, to step up and defend the United States in cyber space.

“I would call on the people here to help us develop defensive capabilities, and frankly, offensive capabilities,” McCain said.

In the wide-ranging conversation, McCain fielded questions from students and shared his views on the conflict in Syria, the Iran nuclear deal, Russia’s imperial ambitions and the pullout of U.S. troops from Afghanistan.

“I study international security, and I feel that his dedication to national security and to veterans have been fundamental, and it was an honor to meet him and hear him talk about these issues,” said Chelsea Green.

The forty students who met with McCain were selected for their special interest in international affairs and politics, and included representatives from the Center for International Security and Cooperation’s honors program, Hoover Institution National Security Mentees and Stanford in Government student group.

International relations major Kayla Bonstrom said she was excited to meet the Senator from her home state of Arizona.

“He was very easy to talk to,” she said.

Bonstrom said McCain’s casual style, which included the occasional joke, helped put the students at ease.

“It was nice to see him in a different setting.”

Mathematical and computation science major Varun Gupta said he was touched by the empathy McCain showed when he shared his experiences visiting refugee camps in war zones.

[[{"fid":"220696","view_mode":"crop_870xauto","fields":{"format":"crop_870xauto","field_file_image_description[und][0][value]":"","field_file_image_alt_text[und][0][value]":"","field_file_image_title_text[und][0][value]":"U.S. Senator John McCain gives an impassioned presentation to students about American foreign policy, as CISAC faculty member Coit Blacker looks on.","field_credit[und][0][value]":"Rod Searcey","field_caption[und][0][value]":"","field_related_image_aspect[und][0][value]":"","thumbnails":"crop_870xauto"},"type":"media","attributes":{"title":"U.S. Senator John McCain gives an impassioned presentation to students about American foreign policy, as CISAC faculty member Coit Blacker looks on.","width":"870","style":"width: 400px; height: 267px; float: left; margin-right: 15px","class":"media-element file-crop-870xauto"}}]]“It was good to see his concern, his actual visceral concern for these issues,” Gupta said.

“It was really great to see the more human side.”

Other students were also impressed by McCain’s sincerity.

“He seems to sincerely believe in all of his views,” said Alexa Andaya, a political science major.

“You can tell when he says something he’s genuine about it.”

Matt Nussbaum, another political science major, said that while he disagreed with many of McCain’s hawkish positions on national security, he welcomed the opportunity to hear the opinions of such a seasoned veteran of foreign policy.

“A lot of times, we’re looking at the academic side of things, and I think that’s very interesting, but Senator McCain and other policy makers use the theory to create policy, so it’s useful to see what they think, how they think and why they think that way,” Nussbaum said.

McCain ended his talk by urging the students to get more involved in politics, whether they were “Democrat or Republican, libertarian or vegetarian.”

He told them that he believed the next presidential election was going to be the most important decision point for the country since 1980, when Republican Ronald Regan defeated Democratic incumbent Jimmy Carter.

“Pick the cause that you want to support, pick the candidate you want to support, and be engaged,” he said.

“It’s your future. You’re the ones that are going to live with the person that you choose to be president of the United States.”

Hero Image
img 3457
Rod Searcey
All News button
1
Paragraphs

The article examines the impact of the summit between President Obama and President Xi on future cybersecurity relations between the two countries, and the changing nature of cyber cooperation and confrontation.

All Publications button
1
Publication Type
Commentary
Publication Date
Journal Publisher
Forbes
Authors
Herbert Lin
0
Affiliate
adam_segal.jpg PhD

Adam Segal is the Ira A. Lipman chair in emerging technologies and national security and director of the Digital and Cyberspace Policy program at the Council on Foreign Relations (CFR). An expert on security issues, technology development, and Chinese domestic and foreign policy, Segal was the project director for the CFR-sponsored Independent Task Force Reports Confronting Reality in Cyberspace, Innovation and National Security, Defending an Open, Global, Secure, and Resilient Internet, and Chinese Military Power. His book The Hacked World Order: How Nations Fight, Trade, Maneuver, and Manipulate in the Digital Age (PublicAffairs, 2016) describes the increasingly contentious geopolitics of cyberspace. His work has appeared in the Financial Times, the New York Times, Foreign Policy, the Wall Street Journal, and Foreign Affairs, among others.

From April 2023 to June 2024, Segal was a senior advisor in the State Department's Bureau of Cyberspace and Digital Policy, where he led the development of the United States International Cyberspace and Digital Policy. Before coming to CFR, Segal was an arms control analyst for the China Project at the Union of Concerned Scientists. There, he wrote about missile defense, nuclear weapons, and Asian security issues. He has been a visiting scholar at the Hoover Institution at Stanford University, the Massachusetts Institute of Technology's Center for International Studies, the Shanghai Academy of Social Sciences, and Tsinghua University in Beijing. He has taught at Vassar College and Columbia University. Segal is the author of Advantage: How American Innovation Can Overcome the Asian Challenge (W.W. Norton, 2011) and Digital Dragon: High-Technology Enterprises in China (Cornell University Press, 2003), as well as several articles and book chapters on Chinese technology policy.

Segal has a BA and PhD in government from Cornell University, and an MA in international relations from the Fletcher School of Law and Diplomacy, Tufts University

CV
Date Label
Authors
News Type
News
Date
Paragraphs

Anything networked can be hacked.

Everything is being networked.

Therefore everything is vulnerable.

That was one of the key takeaways for the 30 Captiol Hill staffers who flew to Stanford University from Washington D.C. last week to attend three days of intensive cybersecurity training at the second Congressional Cyber Boot Camp.

Image
“Whatever level you’re worried about cybersecurity, you should be more worried,” LinkedIn cofounder and Stanford alum Reid Hoffman warned the bipartisan group who staff key congressional oversight committees, during a keynote address with former Secretary of State and Stanford professor Condoleezza Rice.

Silicon Valley executives and entrepreneurs, academics and former high-level government officials painted a picture of a complex threat landscape, where foreign nation states routinely hack into U.S. companies and government agencies with near impunity, and everything from utilities and critical infrastructure, to cell phones and cars could be vulnerable to cyber attack.

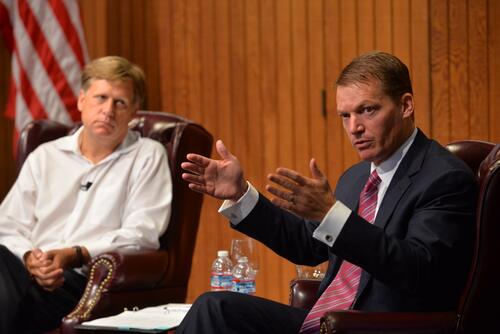
“The next conflict, if it happens tomorrow, it’s not going to be pretty in cyber space,” said Kevin Mandia, president of FireEye and one of the world’s leading experts on counter forensics, in an onstage conversation with Michael McFaul, the former US ambassador to Russia and director of the Freeman Spogli Institute for International Studies.

Mandia said that 29 out of the 30 significant cyber attacks his company was currently investigating were the handiwork of state-sponsored hackers, with the Chinese and Russian governments among the chief offenders.

Image
“The Russian government has been accessing the majority of our government systems in my estimation for most of the last two decades,” he said.

“They can hack any company they choose. They can hack any government agency they choose.

“We’ve spent billions of dollars on defense, but I don’t think we’ve raised the cost of offense a dollar.”

The asymmetrical nature of conflict in cyber space was a common refrain.

“The people that want to attack have distinct and profound advantages over the defender,” said Herb Lin, senior research scholar at the Center for International Security and Cooperation (CISAC) and research fellow at the Hoover Institution.

That’s because finding flaws in commonly used software, which can have more than 40 million lines of code, is like looking for the proverbial needle in the haystack.

“Each one of those lines of logic might have a flaw that can be exploited by an attacker to break in,” said Corey Nachenberg, chief architect of Symantec’s Security Technology and Response division.

“There’s no silver bullet solution…because the attacks are constantly shifting.”

Dan Boneh, a Stanford computer science professor and CISAC affiliate, demonstrated how a seemingly benign sensor, like the one that measures battery life in your iPhone, could be hijacked to pinpoint your exact location.

He also showed how the gyroscope that enables interactive games on your iPhone could be used to measure minute vibrations on a tabletop surface and eavesdrop on conversations.

Even everyday objects like cars can be compromised.

“Our mental models are focused on servers and laptops…but the vast majority of processors that ship every year look nothing like computers,” said Stefan Savage, a professor of computer science and engineering at the University of California at San Diego.

Savage’s research team published pioneering work on car hacking in 2010 that proved it was possible for a hacker to remotely take control of a car’s engine and brakes.

And cars are just the tip of the iceberg.

“There’s probably not a single mode of transportation that’s not controlled by a computer,” Savage said.

His next research target is the aviation industry.

Amy Zegart, CISAC co-director and senior fellow at the Hoover Institution, led a hands-on simulation exercise for visiting congressional staffers, where they assumed the roles of tech company employees responding to a major cyber breach.

Experienced executives from Intel, Uber, and Palo Alto Networks acted as board members and quizzed the staffers on how their assigned departments (including legal, marketing, business strategy and engineering) would manage the crisis.

Image
The three-day boot camp concluded with a behind the scenes tour of Facebook’s new headquarters in nearby Menlo Park, led by the social networking Web site's Chief Information Security Officer (CISO) Alex Stamos.

Zegart said she wanted to expose congressional staff to a diverse range of experts, drawn from the tech industry, legal, technical and policy fields.

“We’ve got to figure out how to accelerate the learning process and work across disciplines,” Zegart said.

Other speakers agreed.

“The time to tackle these difficult policy challenges is now, not after one of these attacks happen,” said U.S. Air Force Col. Matteo Martemucci, division chief for the Joint Staff at the Pentagon.

The Cyber Boot Camp was hosted jointly by CISAC, the Freeman Spogli Institute for International Studies and the Hoover Institution, and co-sponsored by the Stanford Cyber Initiative.

Hero Image
rsd15 065 1065a
All News button
1
Authors
News Type
News
Date
Paragraphs

Thirty congressional staffers are set to get a primer on cybersecurity challenges and countermeasures from some of Silicon Valley’s leading academic, industry and public policy practitioners as part of an intensive three-day workshop to be held at Stanford University from August 17–19.

“Cybersecurity threats are growing more serious and evolving rapidly,” said Amy Zegart, CISAC co-director and Davies Family senior fellow at the Hoover Institution.

Image
“Stanford is in a unique position to bring academic, industry, and policy leaders together to develop new ideas to tackle these challenges.”

The second annual Congressional Cyber Boot Camp is an invitation-only event that will feature lectures from industry experts including LinkedIn cofounder Reid Hoffman, Uber Chief Security Officer Joe Sullivan, Palantir Technologies Global head of Cyber Security Melody Hildebrandt, and Facebook Chief Security Officer Alex Stamos.

Participants will also hear from some of the top academics in the field, including CISAC senior research scholar and Hoover Institution research fellow Herb Lin, and CISAC affiliates Dan Boneh, John Villasenor and John Mitchell.

Image
High-level former government officials will brief participants on real-world and policy problems around cybersecurity issues. Speakers include former Secretary of State Condoleezza Rice, former deputy secretary of Homeland Security Jane Holl Lute, and former U.S. Ambassador to Russia and current director of Stanford’s Freeman Spogli Institute for International Studies Michael McFaul.

Sessions will cover a wide range of topics, from the fundamentals of cybersecurity, to how to think like an attacker, domestic and international legal considerations, and the interplay between cybersecurity and civil liberties.

Zegart will lead a live, hands-on simulation of a cyber attack, with staffers playing the roles of corporate executives responding to the crisis.

“The boot camp is an invaluable experience that brought congressional staff together to deliberate the complex cyber policy issues we’re facing on Capitol Hill and to hear from across academic disciplines different ways to think about these tough problems,” said past participant Brett DeWitt, staff director of the Subcommittee on Cybersecurity, Infrastructure Protection, and Security Technologies.

Image
“Last year’s boot camp provided critical knowledge that has since empowered us to make more well-informed cyber policy decisions and directly supported Congress coming together last December to pass five foundational pieces of cyber security legislation.”

The three-day conference will conclude with a tour of the Facebook’s new headquarters in Menlo Park.

Although the cyber workshop is by invitation only, Hoover, Stanford, and CISAC will provide live updates on Twitter throughout the event. Follow the conversation at #StanfordCyber.

The event will be jointly hosted by CISAC, the Freeman Spogli Institute for International Studies and the Hoover Institution, and is co-sponsored by the Stanford Cyber Initiative.

Hero Image
14967499183 6130ef3de2 o
All News button
1
Subscribe to Cybersecurity